Available for SOC / Blue Team Internships

Nguyen Duc Anh

Information Security/Blue Team/Aspiring SOC Analyst

Defending digital assets through log correlation, threat detection, and analytical rigor. Combining defensive security workflows with secure front-end architecture to build intuitive operational tooling.

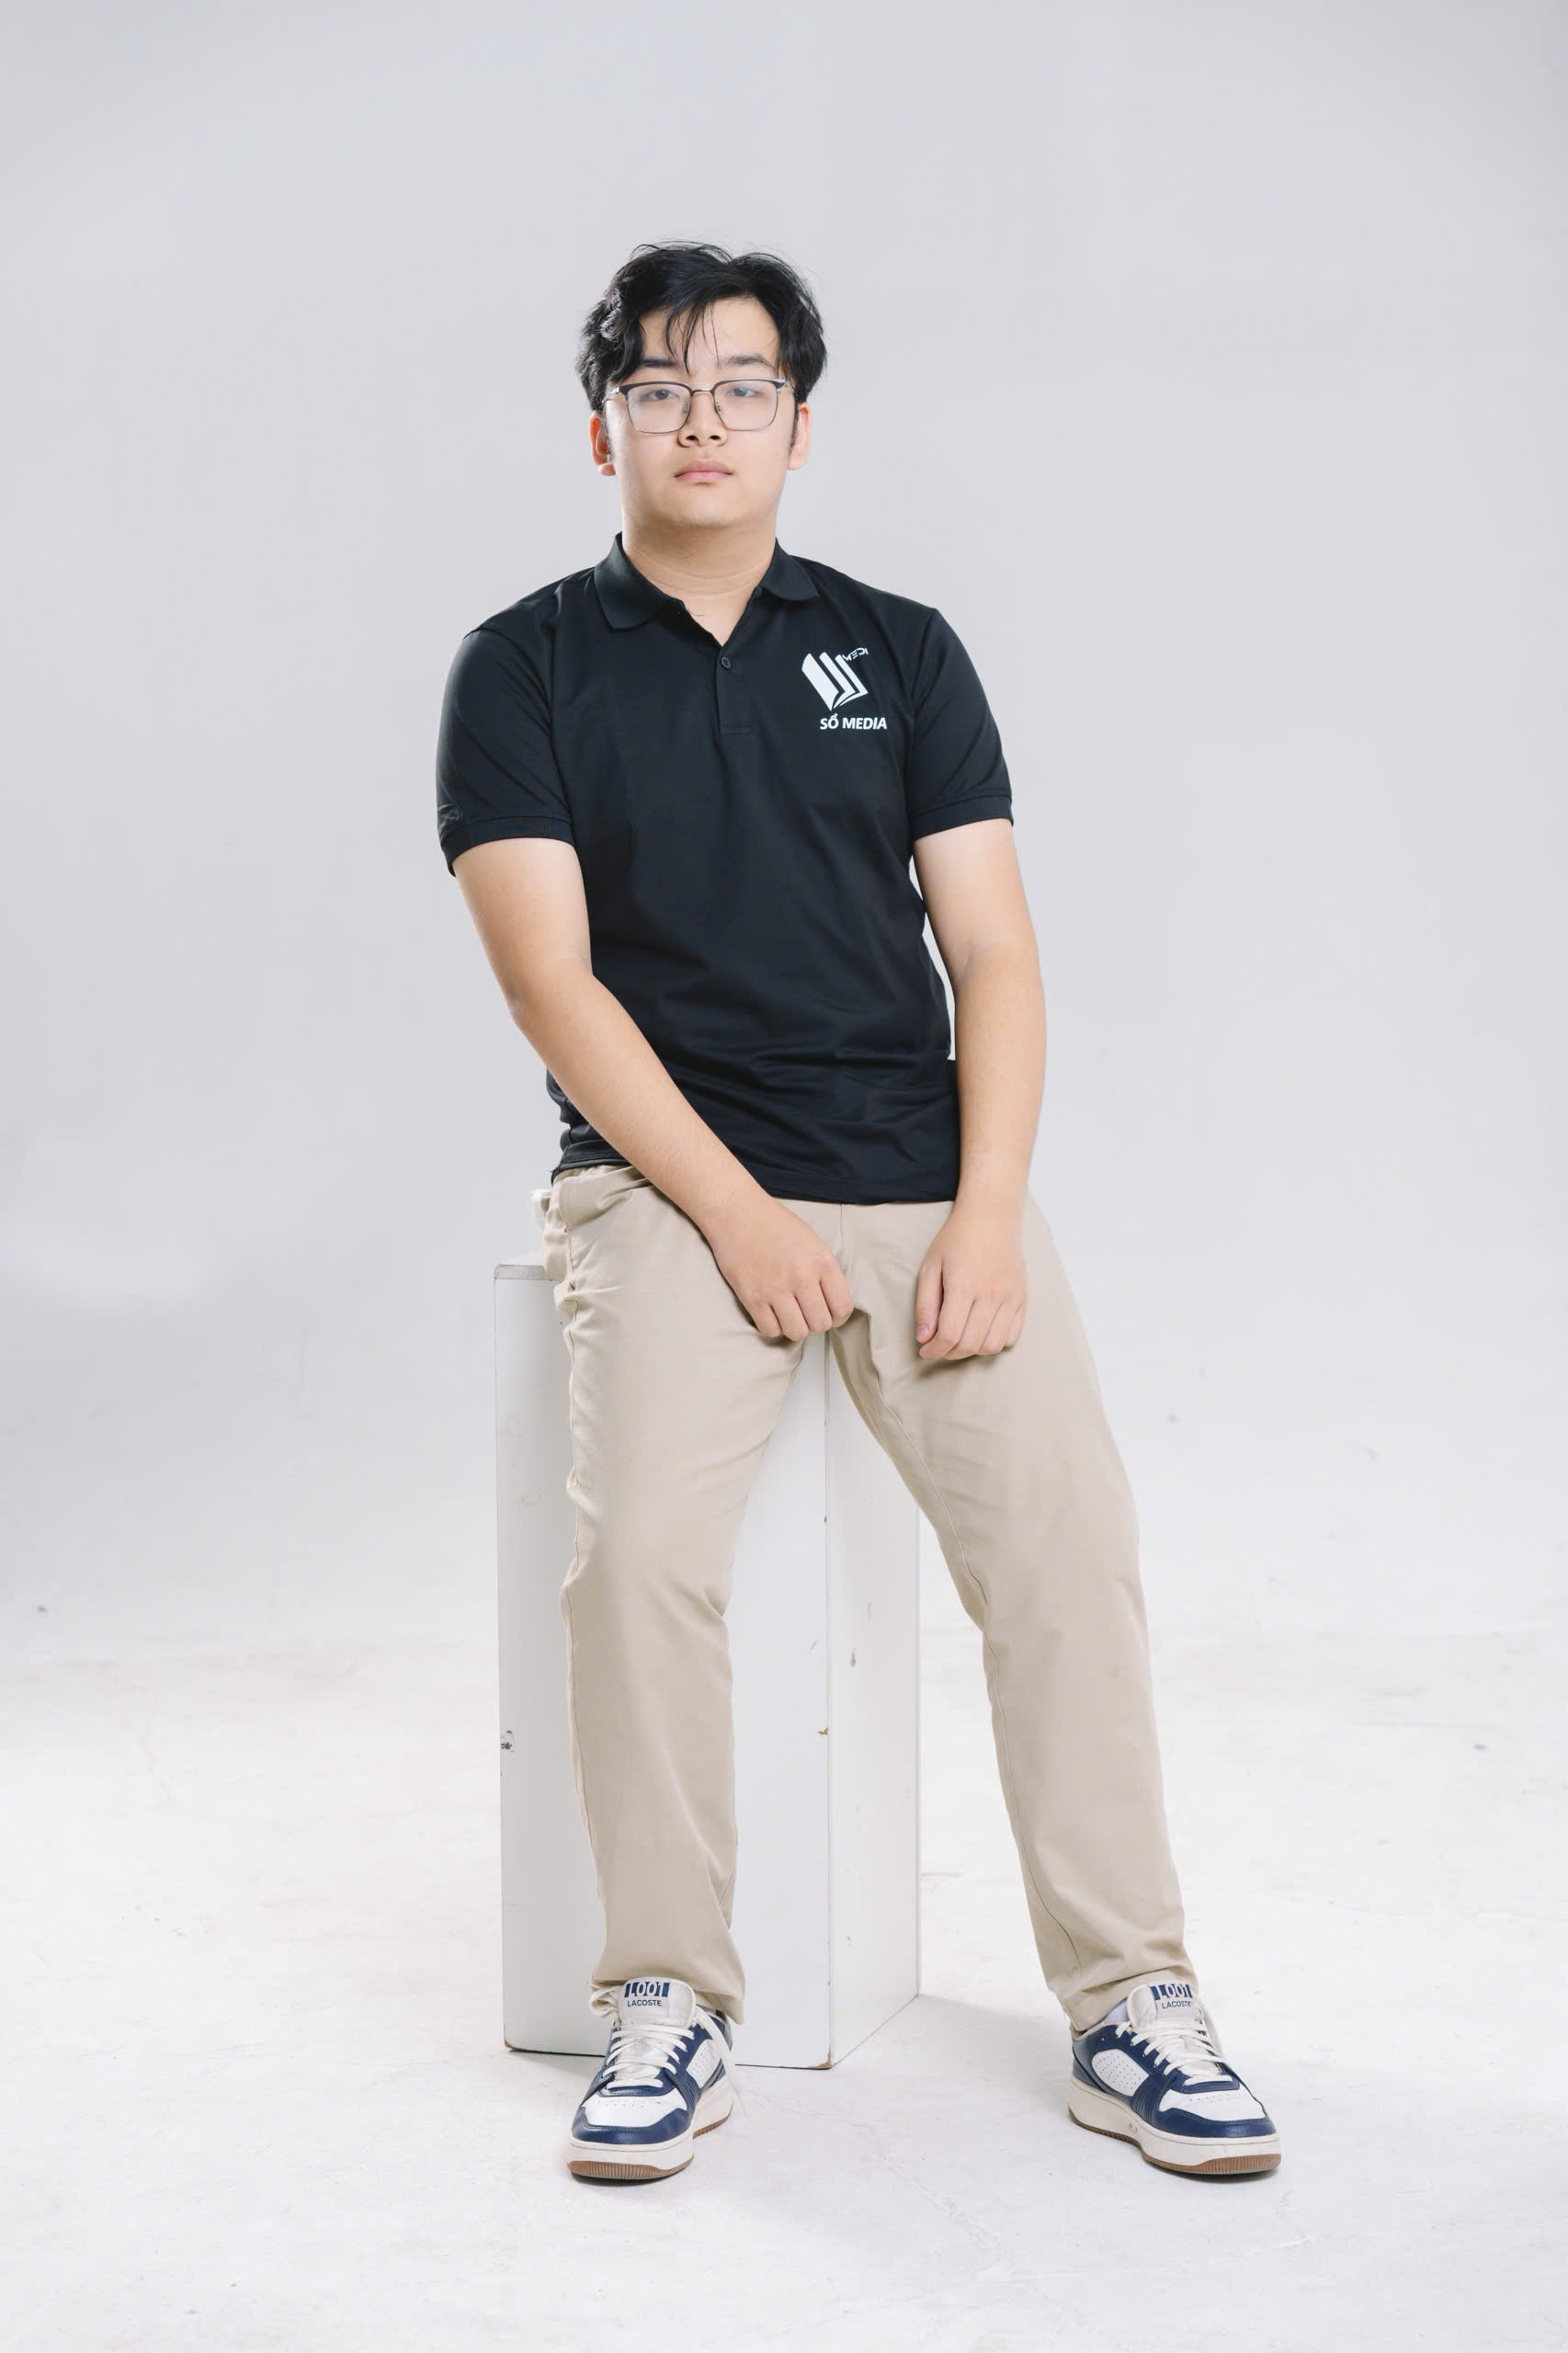
Portrait of Nguyen Duc Anh
01 About

Cybersecurity student at Posts and Telecommunications Institute of Technology (PTIT), Hanoi. My core focus is SOC Operations & Defensive Security — centered on alert triage, telemetry analysis, event correlation, and mapping adversary techniques to detection rules.

I approach security with a structural engineering perspective: understanding low-level OS mechanisms, inspecting web attack vectors, and visualizing telemetry clearly. Combining threat detection logic with secure interface engineering forms the backbone of my technical methodology.
DisciplineDefensive Security
FocusBlue Team / SOC
EducationPTIT Hanoi
EdgeSecure Front-end
02 Capabilities

Two complementary skill sets

01 · Defend

Blue Team & SOC Operations

  • Log Analysis & Telemetry — Windows Event Logs, Sysmon, SyslogCore
  • SIEM Querying & Monitoring — Splunk, ELK StackActive Learning
  • Alert Triage & Incident VerificationActive Learning
  • Network & Packet Forensics — Wireshark, tcpdumpCore
  • Threat Mapping & Detection — MITRE ATT&CK FrameworkActive Learning
  • OS Hardening & Baseline Configuration — Linux & WindowsActive Learning
02 · Build

Secure Web & Interface Engineering

  • Front-end Architecture — HTML5, CSS3, JavaScript (ES6+), TypeScriptCore
  • UI/UX & Dashboard Prototyping — Figma, Design SystemsCore
  • Web App Security — CSP, Input Sanitization, RBAC UICore
  • Performance Optimization & WCAG AccessibilityCore
03 Focus

Technical Competencies & Domains

log-triage sysmon-analysis detection-engineering incident-response wireshark-pcap SIEM-splunk-elk MITRE-ATT&CK system-hardening secure-frontend-dev
04 Education

Posts and Telecommunications Institute of Technology

PTIT · B.Sc. in Information Security · 2025 – 2030

Building core competencies in defensive security — computer networking fundamentals, OS internals, vulnerability analysis, and security operations protocols.

05 Contact

Get in touch

Open for SOC / Blue Team Internship opportunities. Always eager to connect regarding log triage, detection logic, or secure web architecture.